Open Source · Apache 2.0 · v1.8.0
Stop DDoS floods in seconds with one binary.
Kapkan reads the traffic stats your routers already export (NetFlow, IPFIX, sFlow), spots a flood against the IPs you protect within seconds, and stops it: by telling your router to drop the attack, or by dropping it itself in the Linux kernel. Free, open source, and in watch-only mode until you say otherwise.
One Go binary · Nothing else to install · Watch-only by default · IPv4 + IPv6
- ≥20M flows/sec/core
- Detects in seconds
- IPv4 + IPv6 blackhole
- FlowSpec RFC 8955/8956
- One static binary
How it works
One binary, nothing else to run: no extra services, no message queue, no database. Point your routers at it and go.
- 01
INGEST
Point your routers at Kapkan. They already send a summary of every traffic flow (NetFlow, IPFIX or sFlow), so just aim it at Kapkan's port. One process reads it all; there's nothing else to install.
- 02
DETECT
Kapkan counts packets, bits and connections per second for each IP you protect. Cross a limit you set, or one it learned from that host's normal traffic, and that's an attack, flagged within seconds.
- 03
MITIGATE
Kapkan tells your router to drop the attack over BGP. It can null-route the whole target IP (RTBH), or drop only the attack traffic and keep the rest flowing (FlowSpec). Once the flood stops, it removes the rule itself.
- 04
DROP
Or skip the router: if the traffic crosses the machine Kapkan runs on, it can drop the attack itself inside the Linux kernel (XDP), the moment packets arrive. Every rule has an expiry the kernel enforces, so a crashed Kapkan can't keep dropping your traffic.
What it does
Detection, mitigation, an operator console and the safety rails to run it in production, in one Apache 2.0 binary. Commercial flow-DDoS products sell these as separate modules.
- Reads the flows you already export
- sFlow v5, NetFlow v5/v9 and IPFIX over UDP, read by Kapkan itself. No extra service to run.
- Spots floods in under a second
- Packet, bit and flow-per-second limits over a sliding window, corrected for sampling. ≥20M flows/sec per core.
- Blackhole, or drop just the attack
- Null-route the whole target IP (RTBH), or drop only the attack traffic and keep the rest (FlowSpec). Full IPv6 support, on par with IPv4.
- Tells you what kind of attack
- Amplification (NTP/DNS/memcached), SYN/UDP/ICMP floods, each with a plain 'why this fired' breakdown.
- Learns each host's normal
- Kapkan learns what normal traffic looks like for every host and tightens the limits on its own. No hand-tuning.
- Hard to misfire
- Starts in watch-only mode. Every block has an expiry and lifts itself, a cap limits how many hosts can be blocked at once, and your protected list is never blocked, not by Kapkan and not by you.
- Catches carpet-bombing
- Spots low-and-slow floods spread across a whole IP range that stay under any single host's limit.
- Watch it from anywhere
- REST API, Prometheus /metrics, and alerts over Telegram, Slack, email, webhook or a script you run.
- Multi-tenant & audited
- Scope access per tenant, hand out viewer/operator API tokens, and get an audit log that names who did what.
- In-kernel mitigation with XDP
- Instead of asking a router to drop the attack, Kapkan can do it itself. The same rules it would announce as FlowSpec load straight into the Linux kernel and run there (XDP), including a separate rate limit for each attacking source, which BGP FlowSpec can't do. Needs Linux 5.15+, compiles nothing on the box, and every rule expires inside the kernel, so a crashed Kapkan can't leave your traffic dropped. Still watch-only by default. See how in-kernel drop works
The operator console
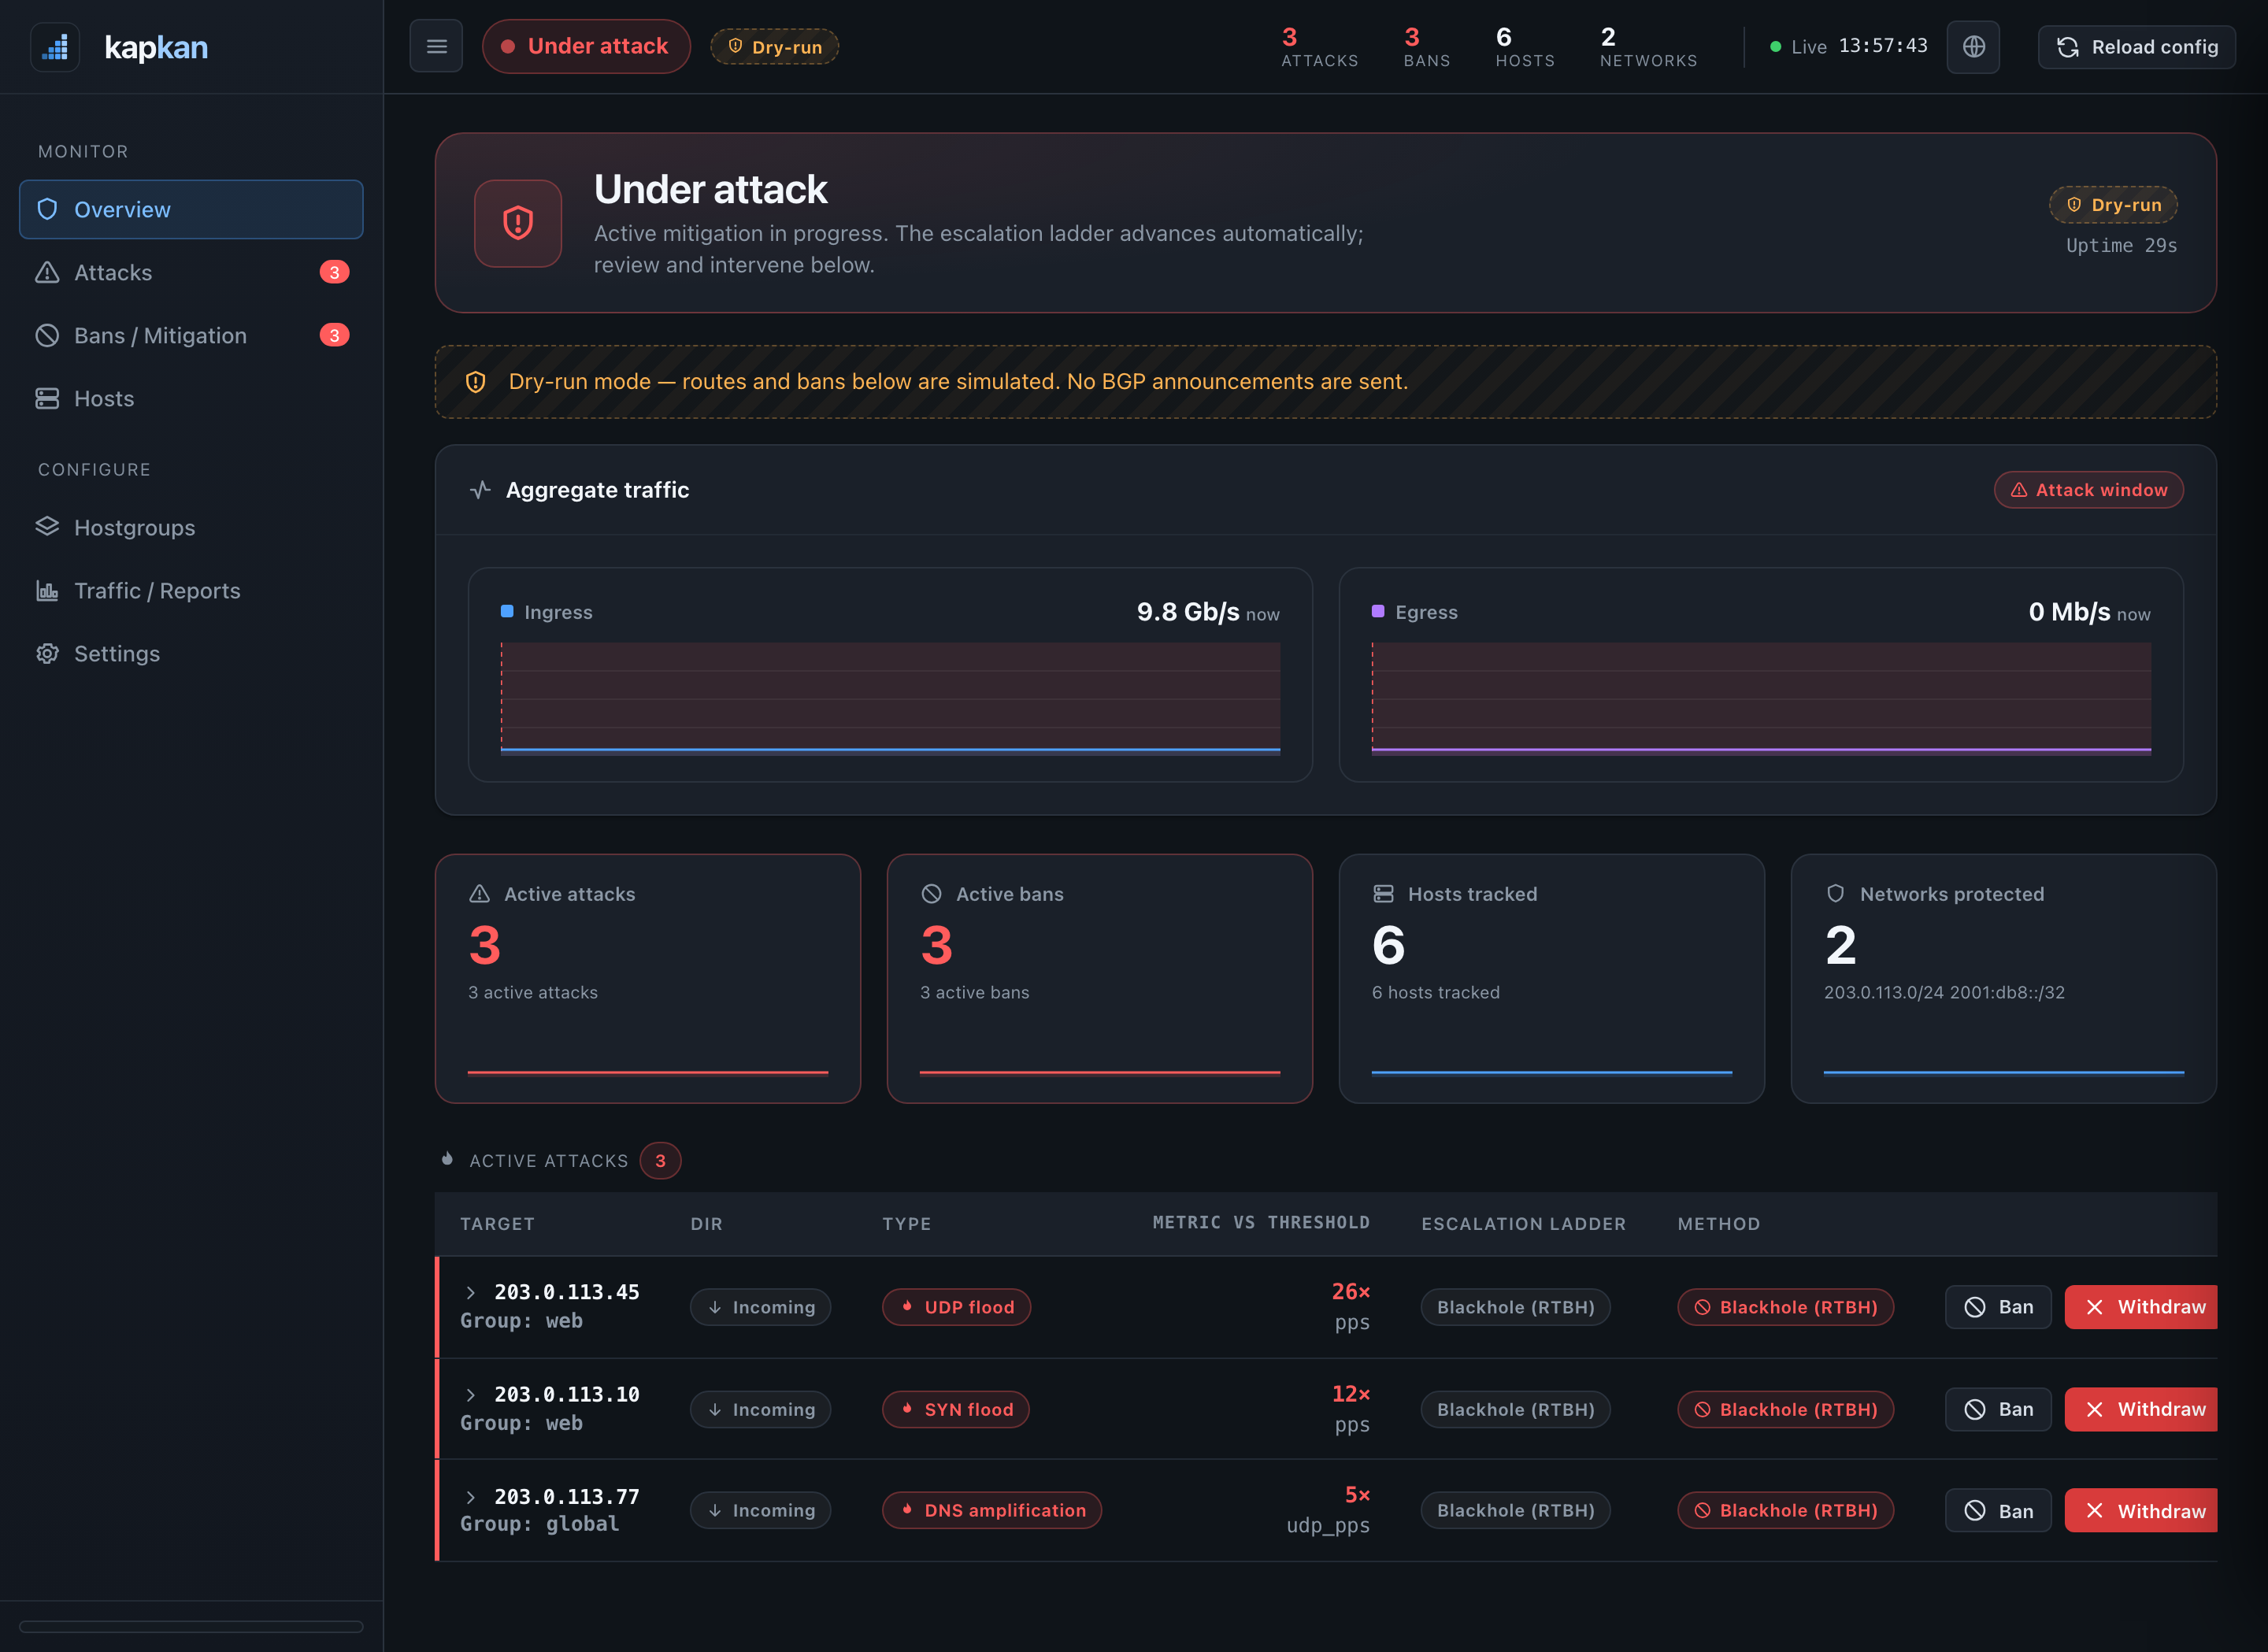
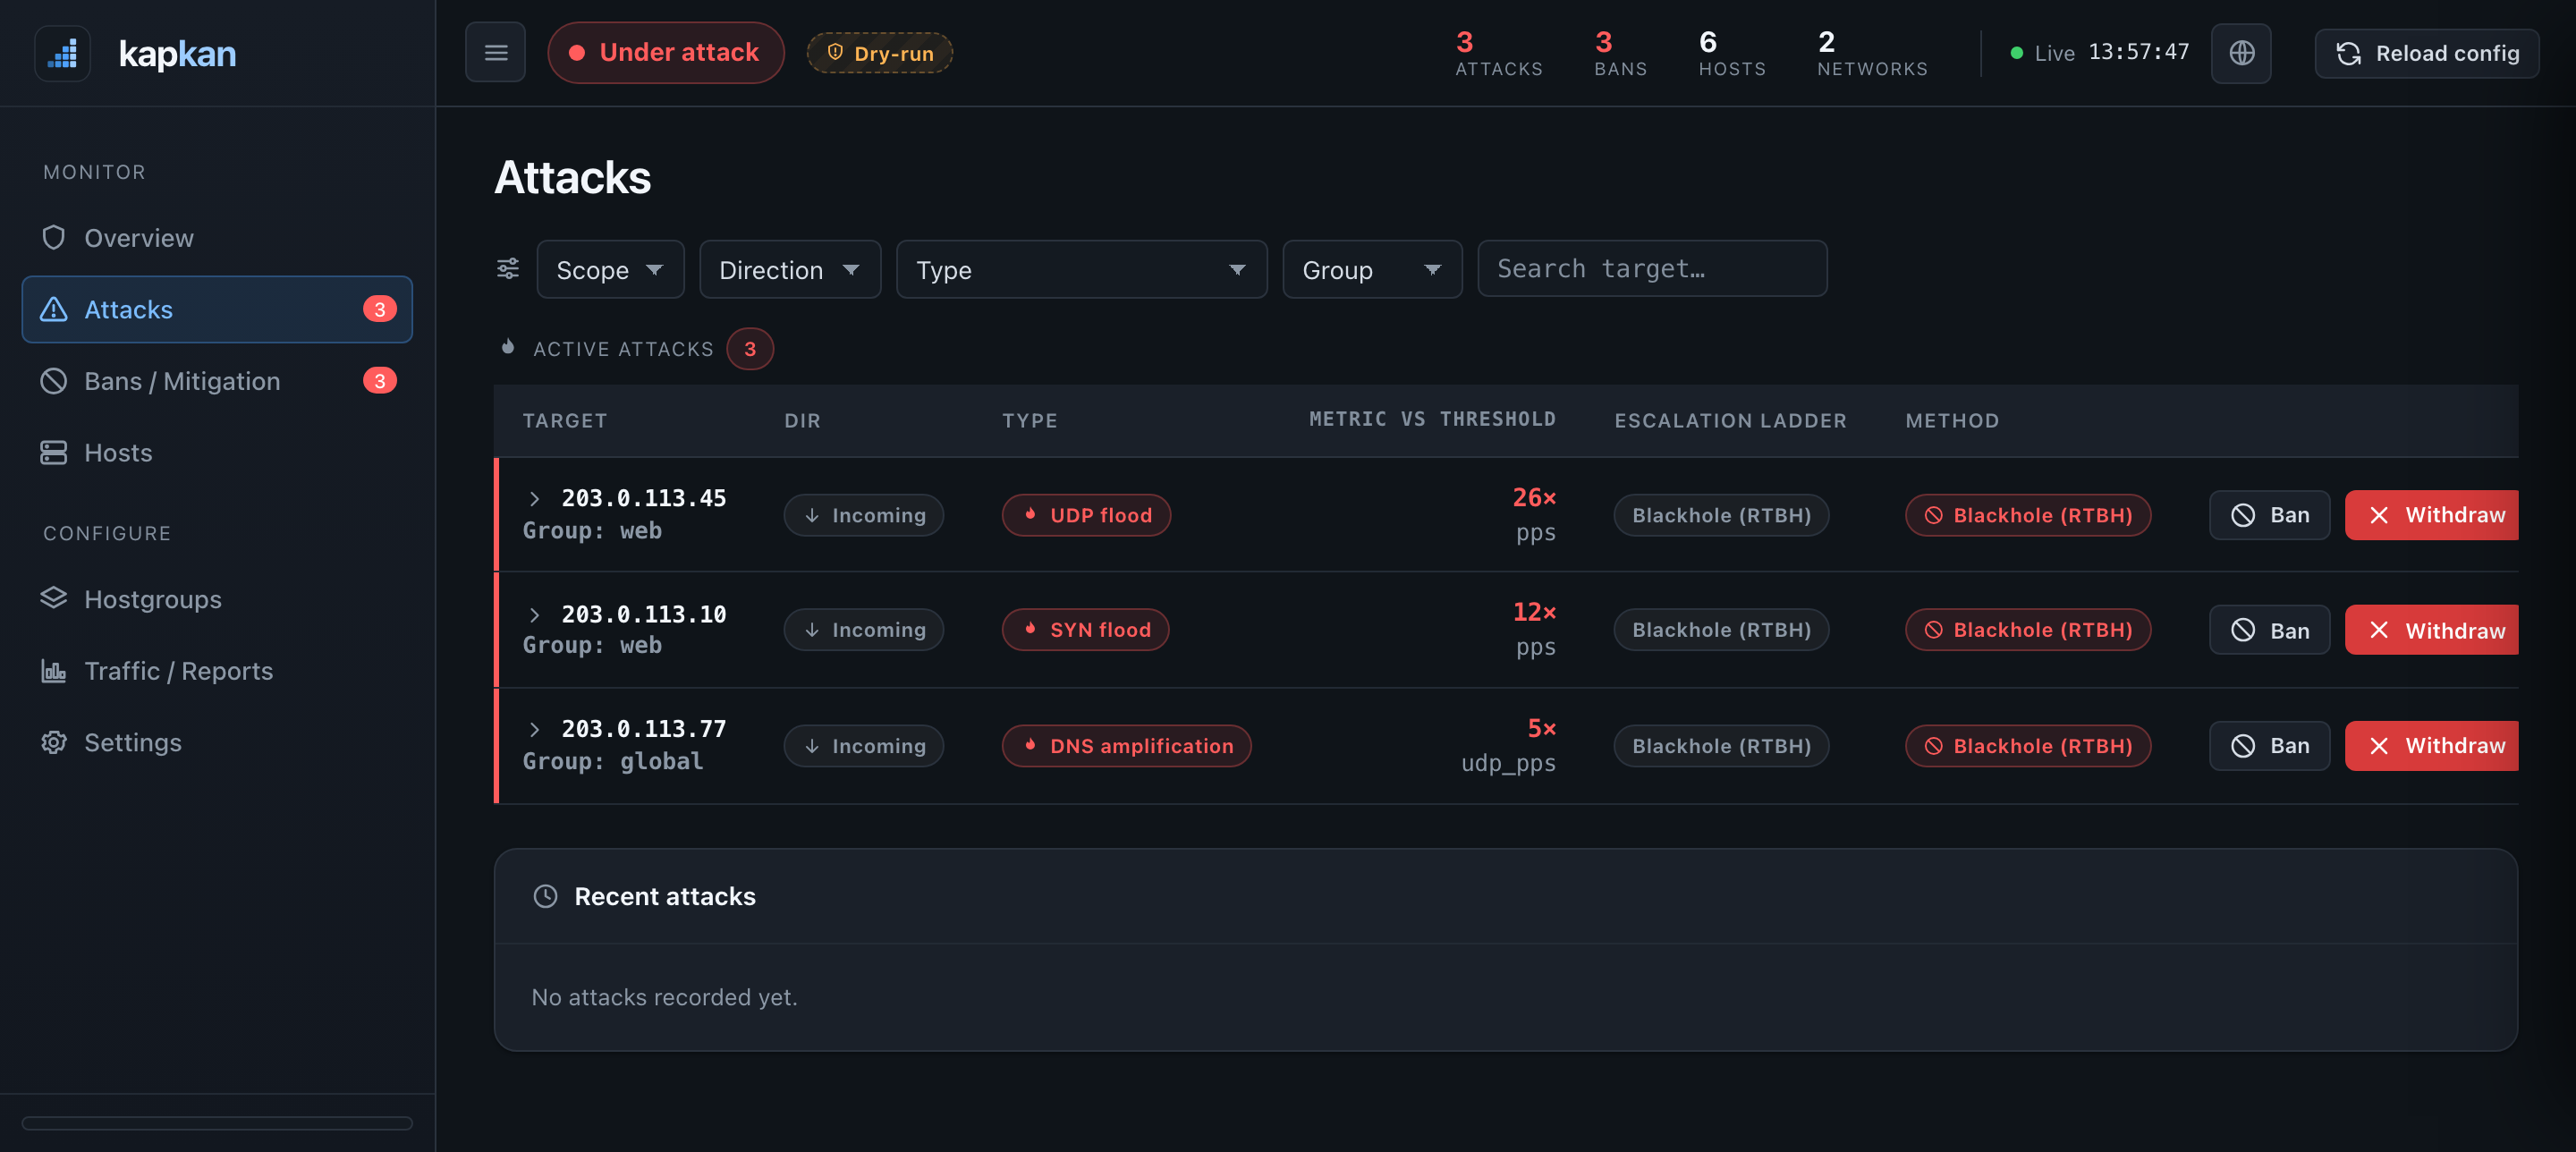
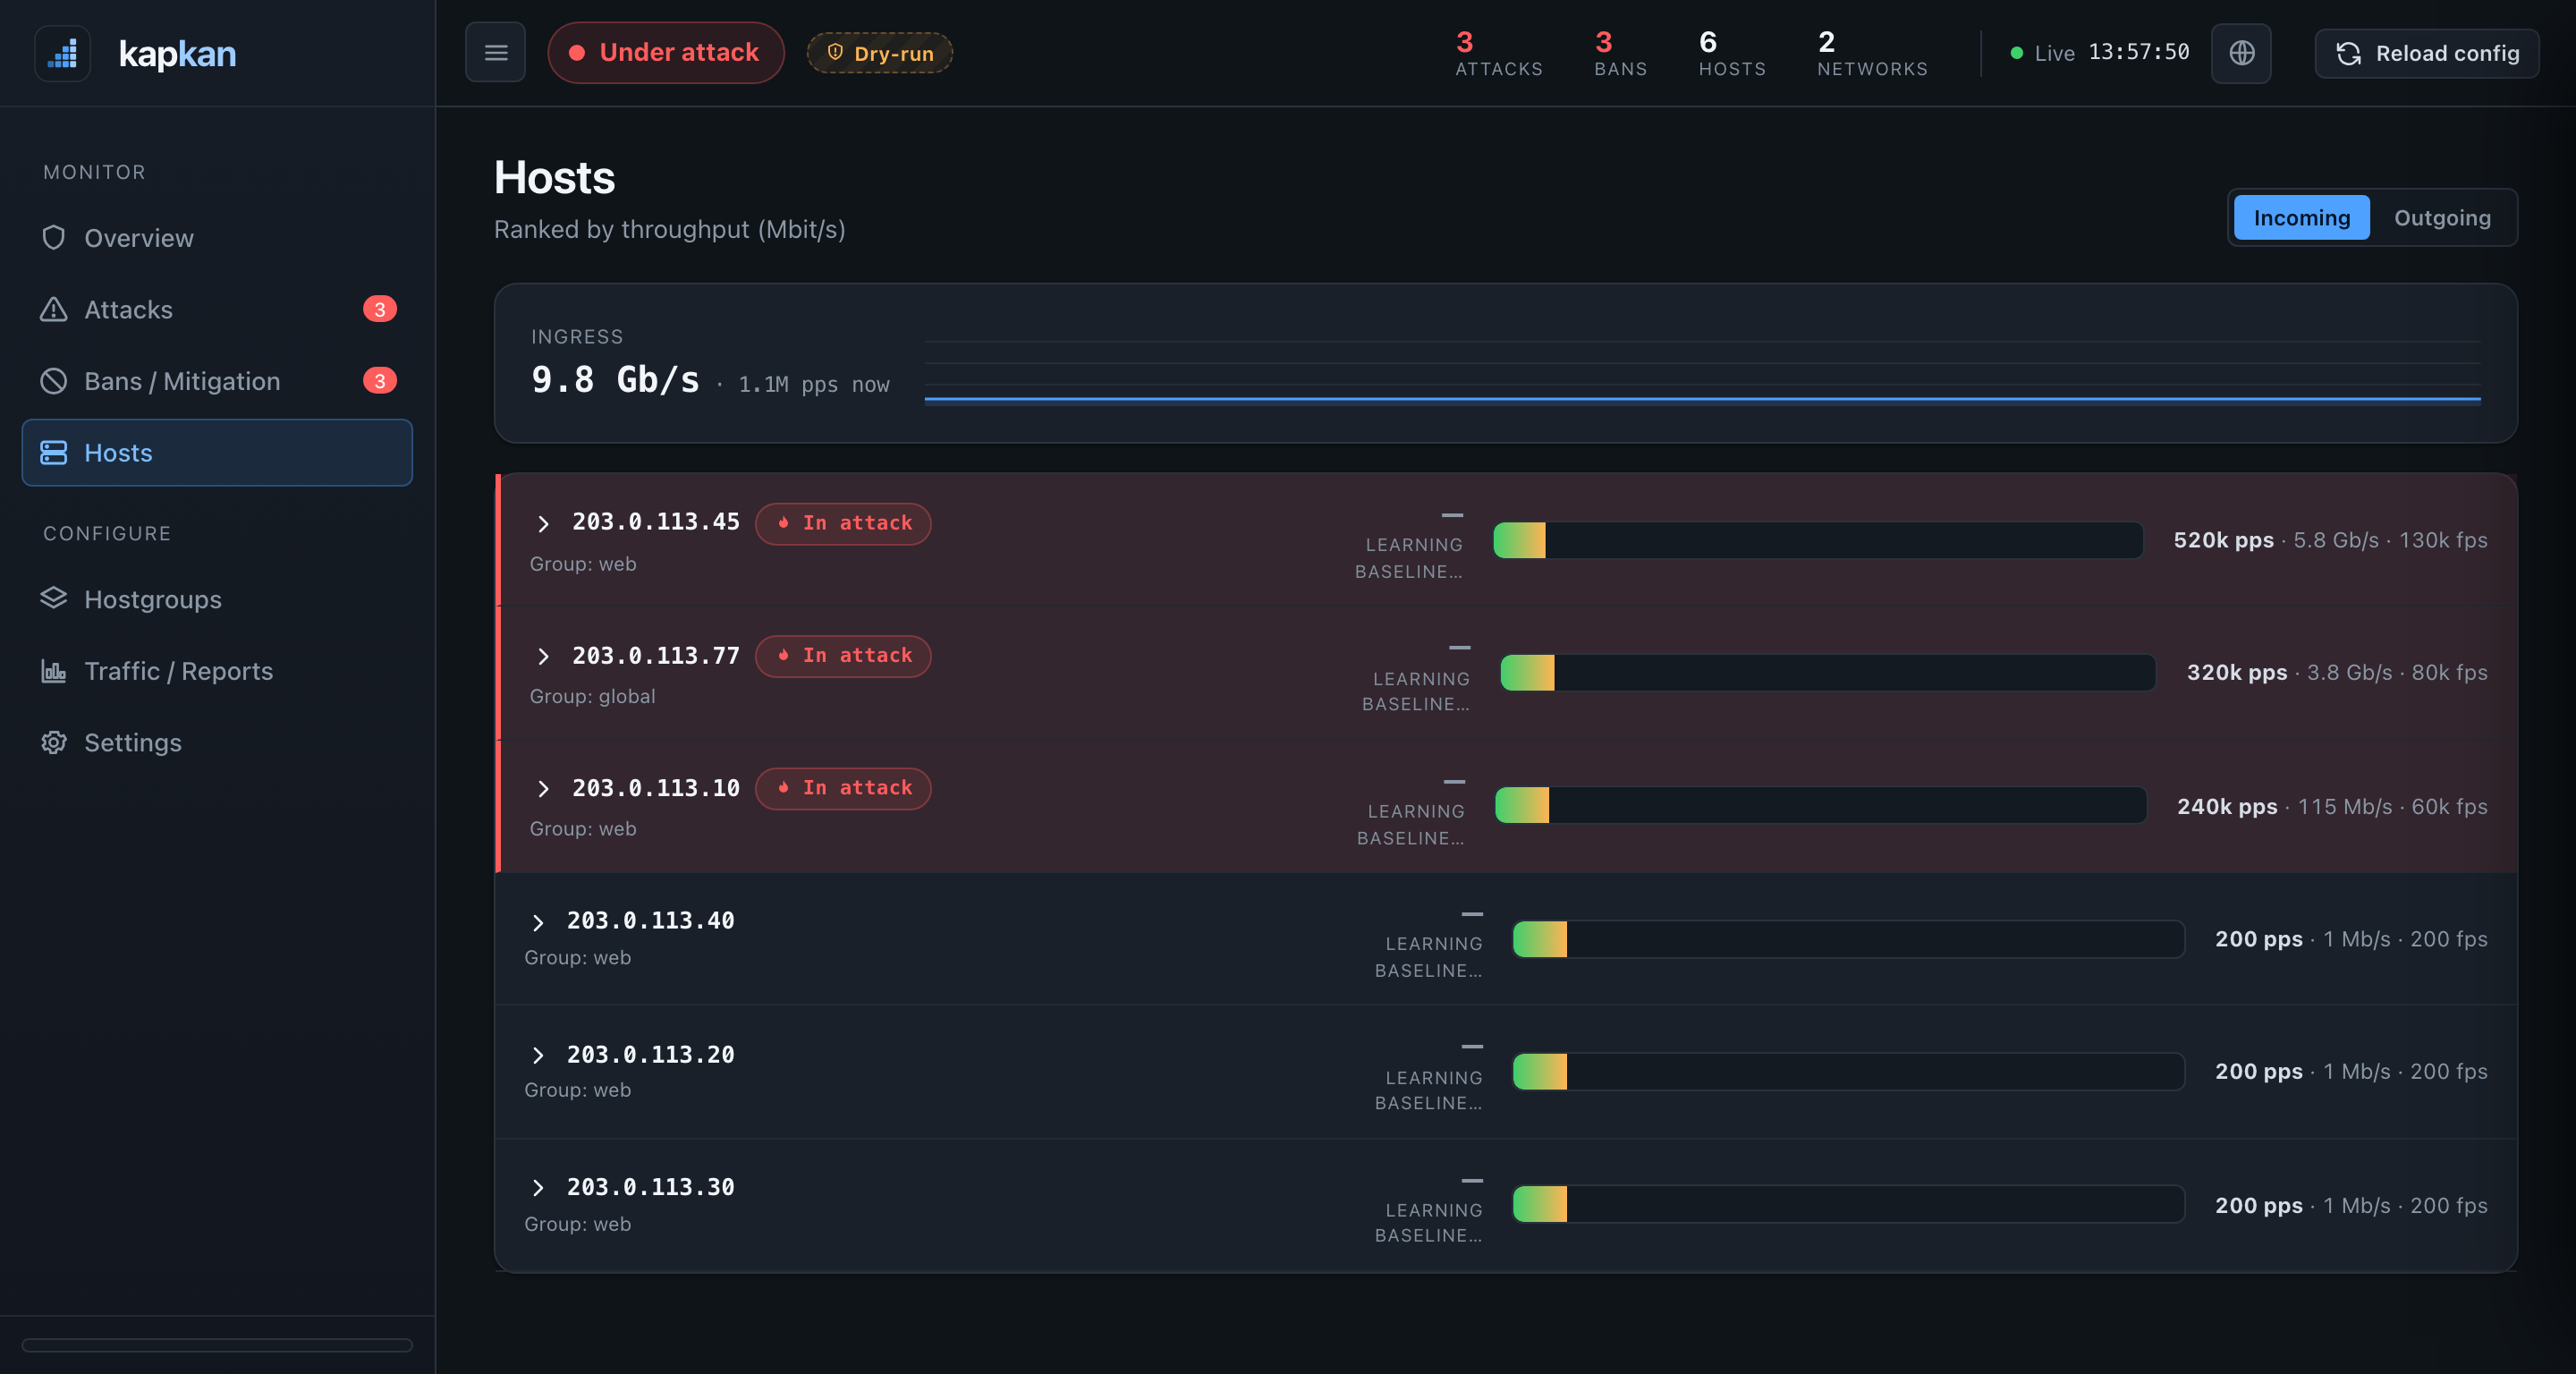
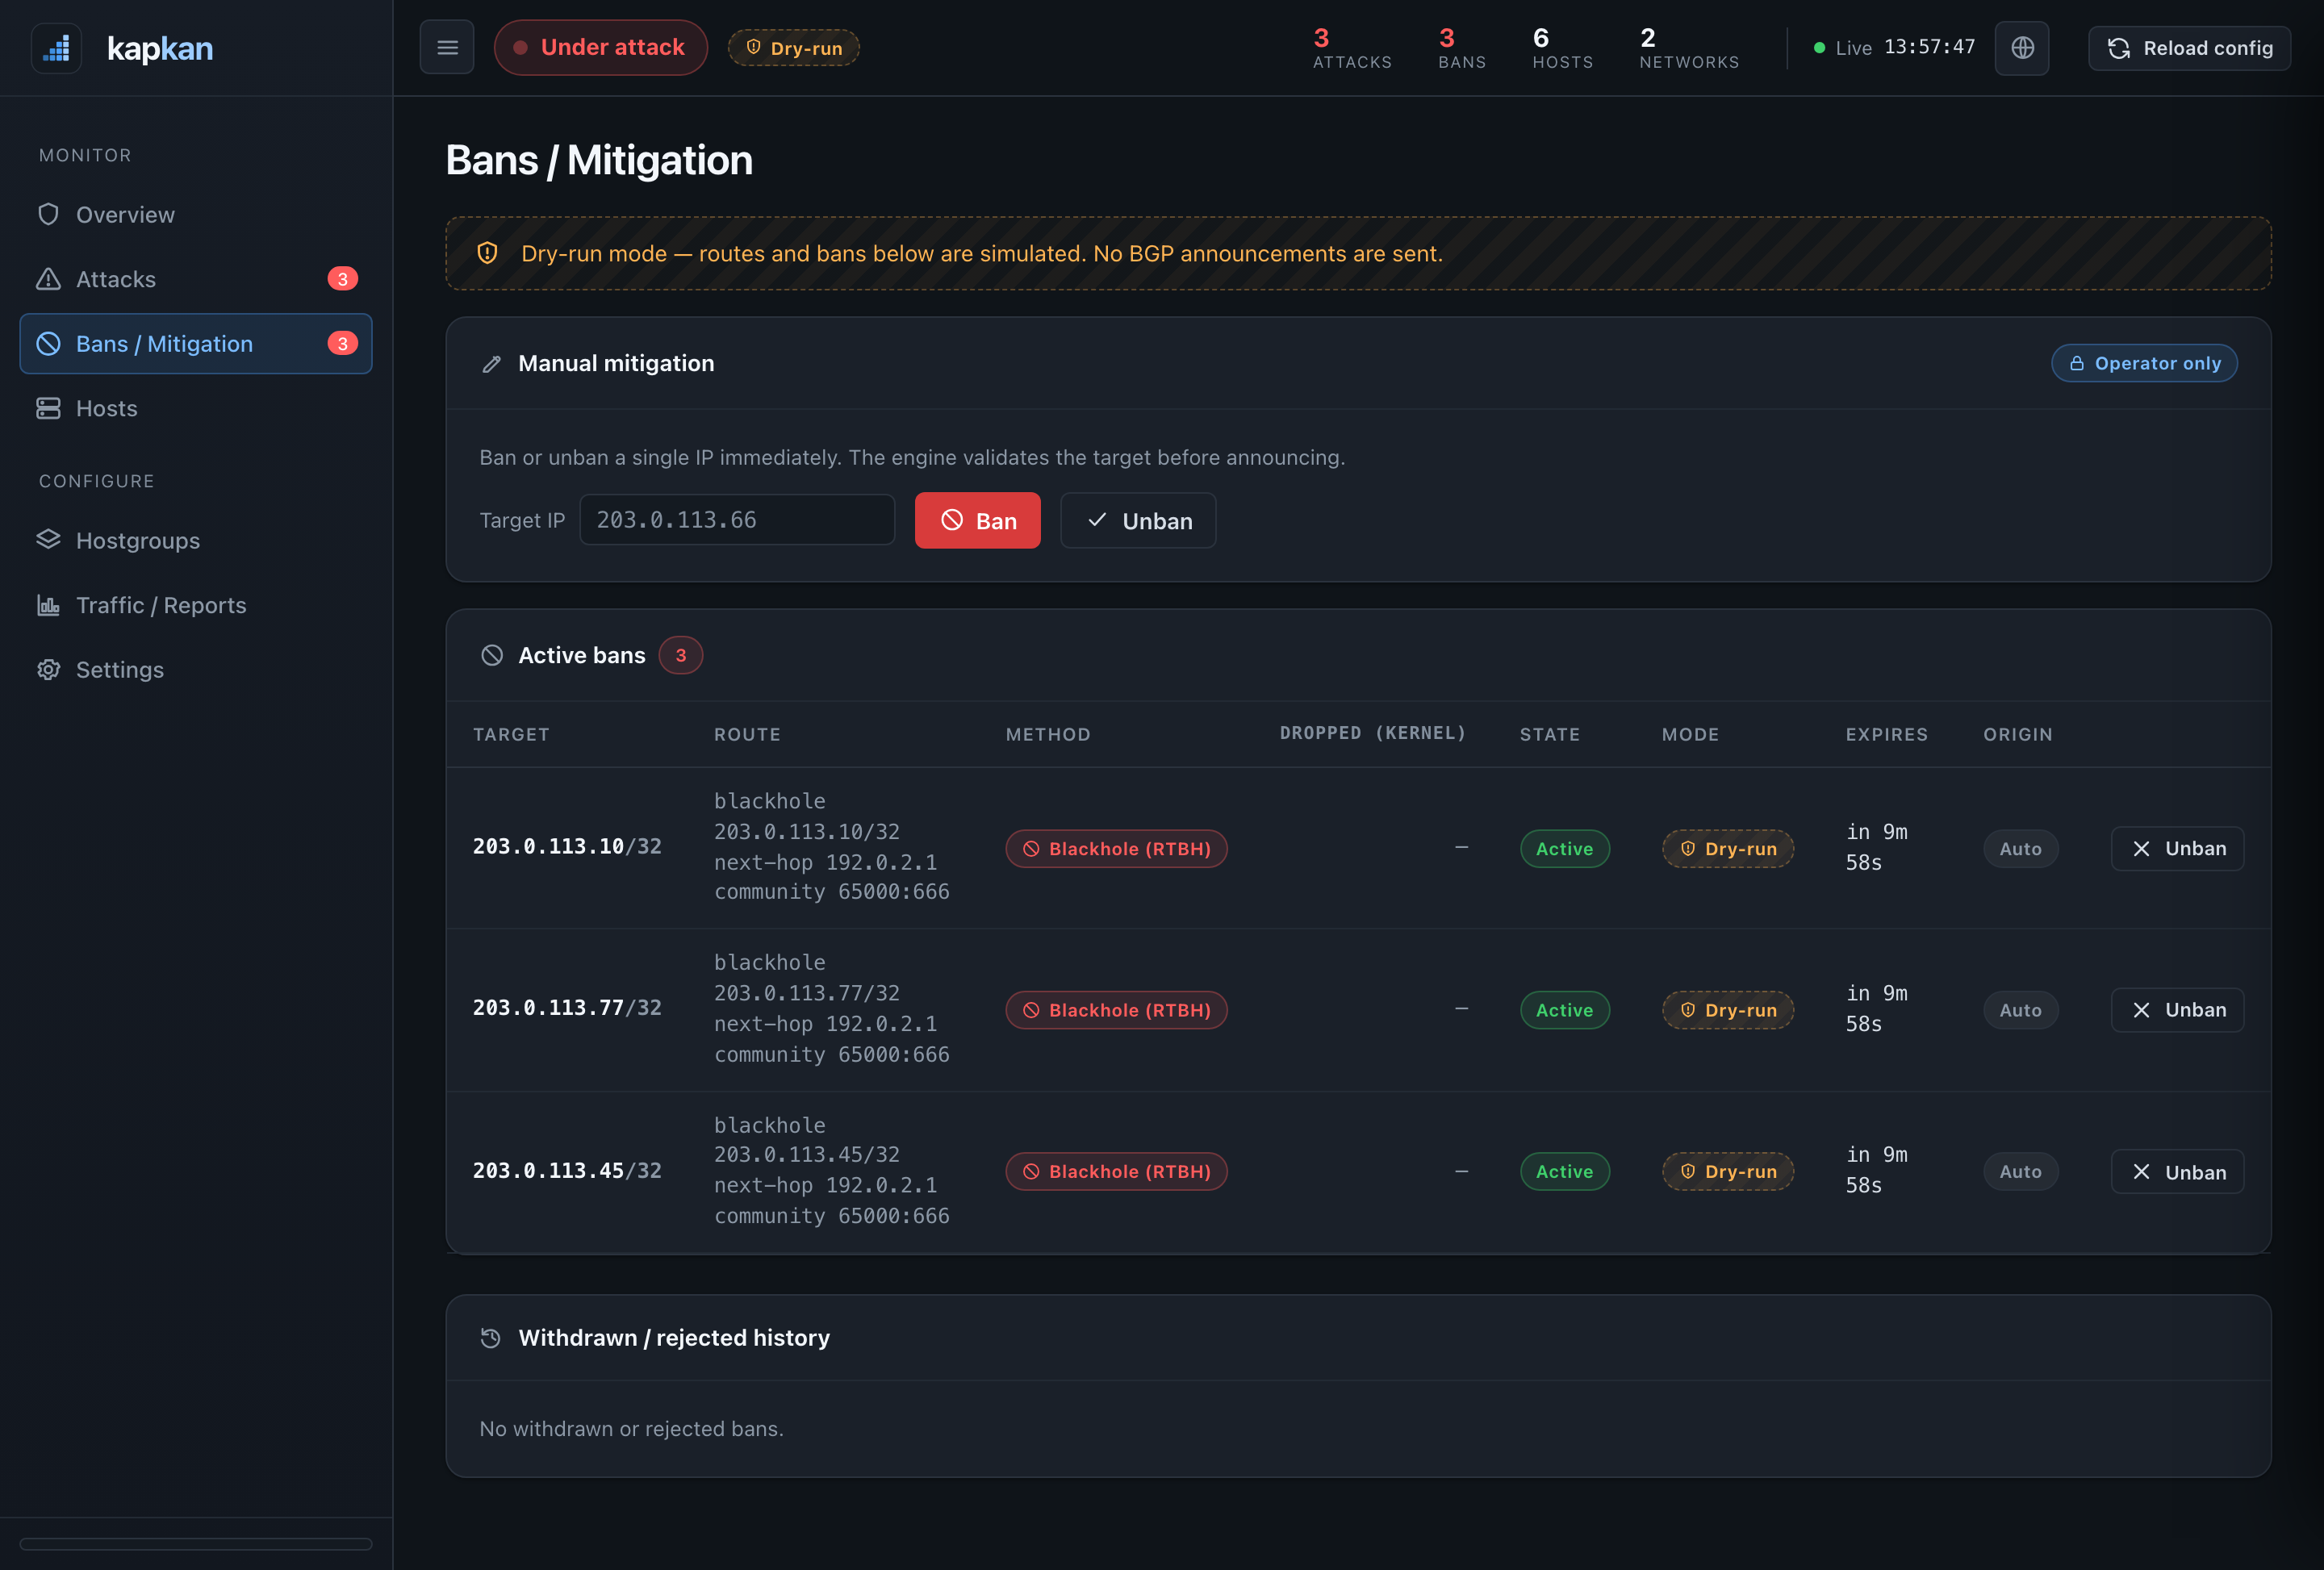
Kapkan ships with a live web console for your on-call: attacks, hosts and blocks in one place. No digging through raw logs.
Compared with commercial tools
One static binary instead of a licensed appliance and a set of daemons.
| Feature | Kapkan | Commercial tools |
|---|---|---|
| License | Free & open source (Apache 2.0) | Paid license / volume-based |
| Operator console | Included free | Paid add-on |
| IPv6 support | Full, same as IPv4 | Missing or planned |
| Threshold tuning | Learns automatically | Offline calculator, copy-paste |
| Automation | Escalation rules in config | Custom bash scripts |
| Architecture | One static binary, no extras | Several daemons to run |
| In-kernel drop | Built in, drops in Linux itself (XDP) | Separate scrubbing appliance |
Running in minutes, watch-only first
Kapkan is safe to run out of the box. It logs every block it would make and shows it in the API and console, but never announces anything to your routers until you explicitly set dry_run: false.
$ kapkan -config config.yaml
---
dry_run: true
networks: ["203.0.113.0/24"]
thresholds: { pps: 80000, mbps: 1000 }
bgp: { local_asn: 65010, community: "65010:666" }
Set the trap
Free, Apache 2.0, running in an afternoon. Start in watch-only mode and see what it would have blocked.
VER=v1.8.0
curl -fLO \
  "https://github.com/fornex/kapkan/releases/download/$VER/kapkan_${VER#v}_linux_amd64.deb"
sudo apt install "./kapkan_${VER#v}_linux_amd64.deb"